SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
-
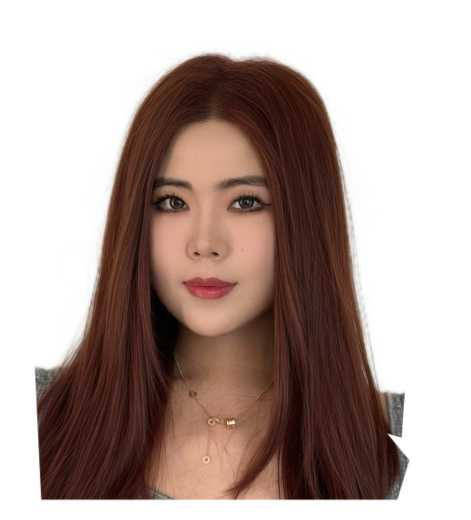 Member of Technical Staff, OpenAI
-
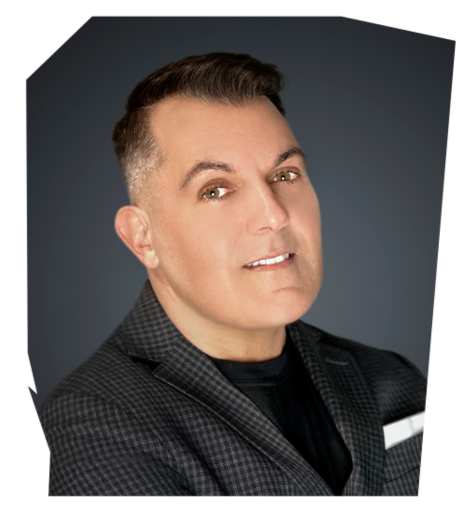 Cyber Behavioral Profiler, FBI (Ret.) and Modus Cyberandi
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, October 21, 202610:30 amExhibitor Hall openRegistration Level:
- Open Sessions
10:30 am - 5:00 pmLocation / Room: Exhibitor HallYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible! Peruse the many downloadable resources each booth has to offer.
11:00 am[Opening Keynote] Building Intelligence Teams in the Age of Agentic AI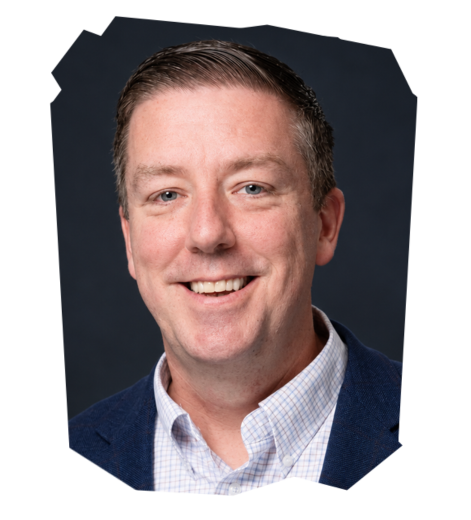 Head of International Security Cooperation, Google CloudRegistration Level:
- Open Sessions
11:00 am - 11:45 amJoin us for a discussion on how Google structures its threat intelligence teams to make the most of agentic AI support to experts and what enterprises should expect as CTI work moves to agent-first. Particular attention will be paid to identifying, training, and retaining the best talent to work in agentic AI-centric CTI teams.
11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmLocation / Room: Exhibitor HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pmBeyond Login: Designing Identity Controls for Modern Enterprise ProductsMember of Technical Staff, OpenAIRegistration Level:- Open Sessions
12:00 pm - 12:45 pmEnterprise identity can no longer be reduced to a login gate. Modern products span admin consoles, workspaces, APIs, and privileged workflows, often across multiple identity providers and assurance levels. This session presents a vendor-neutral architecture that separates principal eligibility, resource authentication requirements, and session assurance. It examines common failures in coarse-grained SSO and shows how teams can introduce stronger controls using policy evaluation, shadow decisions, decision logging, staged enforcement, and rollback safeguards without causing widespread access failures or creating brittle user experiences.
Attendees will leave with a practical architecture and rollout checklist for building resource-aware authentication and authorization controls across complex enterprise products.
12:00 pmRethinking Threat Defense: The Assumptions Behind Modern Security CDO & CDTO | Board Member & Advisor | PodcasterRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmModern security architectures are built on assumptions—about identity, trust, attacker behaviour, analyst workflows, and the boundaries between systems. Those assumptions weren’t mistakes; they were the foundation upon which effective security programs were designed.
As AI reshapes both offensive and defensive capabilities, many of the conditions surrounding those assumptions are beginning to change. The question for security leaders isn’t whether to abandon existing approaches, but how to recognize which assumptions continue to serve us, which deserve to be revisited, and what that means for the future of threat defense.
Rather than focusing on the latest AI tools or attack techniques, this session explores a broader question: how should we think about threat defense when the environment itself is changing? Through the lens of systems thinking, resilience, and organizational adaptation, we’ll examine how AI is influencing the assumptions that underpin modern cybersecurity—and why revisiting those assumptions may become an increasingly important part of building resilient organizations.
12:00 pmDefending the Agentic EnterpriseA Practical Security Model for AI Agents, Identities, and Machine-to-Machine Threats Cloud Solutions Architect, FirstDay FoundationRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmAs AI agents gain access to enterprise applications, APIs, sensitive data, and automated workflows, security teams must defend a new class of autonomous identities. This session presents a practical framework for securing the agentic enterprise by establishing clear human-to-agent-to-tool trust boundaries. It explores least-privilege access, scoped credentials, authorization controls, human approval for high-risk actions, and behavioral monitoring for abnormal agent activity. The session examines how existing Zero Trust, IAM, API security, and cloud security practices can evolve to address agentic threats while enabling responsible AI adoption without creating another isolated security program or adding unnecessary operational complexity.
Attendees will leave with a practical framework to secure AI agents through identity controls, Zero Trust principles, least-privilege access, human oversight, and behavioral monitoring.
12:00 pmWhen Reality Lies: Deepfakes and the Evolution of Phishing APT Head of Threat Intelligence Lead, KnowBe4Registration Level:
- Open Sessions
12:00 pm - 12:45 pmThis session breaks down how AI is reshaping phishing, now driving 84% of attacks, and walks through a real APT case study at a 4,000-employee finance firm. It covers the attack’s multi-stage playbook: high-volume noise campaigns, a fake Microsoft credential-harvesting alert, advanced evasion tactics, and escalation to direct phone contact from the attackers. It closes with the core message: phishing is still the top attack vector, AI has lowered the barrier to entry, and defense demands ongoing education, testing, and patching.
What you will learn:
- Real APT threat intelligence, not just trend commentary
- Tactical detail on evasion and escalation techniques they need to defend against
- Detailed description on how to stay secure
12:45 pmNetworking BreakRegistration Level:- Open Sessions
12:45 pm - 1:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:00 pmZero Trust for AI Agents: Designing Secure Autonomous Systems Software Engineer, JPMorgan ChaseRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmAgentic AI is transforming how enterprises automate decision-making and complex workflows, but it also introduces new security and governance challenges. This session explores the evolving threat landscape for autonomous AI systems, including risks related to LLMs, multi-agent architectures, Retrieval-Augmented Generation (RAG), tool integrations, and data protection. Attendees will gain practical insights into implementing guardrails, governance, observability, and security best practices to build trustworthy, resilient, and enterprise-ready AI solutions that balance innovation with risk management.
1:00 pmThe Deepfake Kill Chain: How Synthetic Candidates Infiltrate Your Hiring ProcessCyber Behavioral Profiler, FBI (Ret.) and Modus CyberandiRegistration Level:- Open Sessions
1:00 pm - 1:45 pmJust like a cyberattack, a deepfake hiring scam follows a predictable sequence of stages—from reconnaissance and identity fabrication to interview deception and, ultimately, insider access. In this session, we’ll walk through the Deepfake Kill Chain step by step: how bad actors research targets, construct synthetic identities, pass video interviews using real-time face-swapping and voice cloning, and slip past traditional background checks. We’ll examine real-world case studies, break down where each stage can be detected and disrupted, and show how organizations can build defenses at every link in the chain—before a synthetic candidate ever becomes an employee.
1:00 pmPick Your Poison: Unmasking the Modern Threat Landscape VP, Global Threat Intelligence, Doppel
 Sr. Manager, Intelligence, ZscalerRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmAdversaries no longer knock on the perimeter—they log in with valid session cookies, impersonate your C-suite with AI, and weaponize shadow SaaS workflows. When your budget, time, and bandwidth are maxed out, which fire do you actually fight?
In this interactive “this or that” showdown, intelligence leaders step into the hot seat to tackle four no-holds-barred dilemmas facing enterprise defense today. Each round presents two catastrophic, highly-realistic threats where they are forced to remediate one and accept total risk on the other. Expect candid debate, live audience polling, and zero buzzwords as we dissect external brand weaponization versus internal encrypted traffic, stolen tokens versus edge proxies, and the shifting reality of cyber extortion.
1:45 pmNetworking BreakRegistration Level:- Open Sessions
1:45 pm - 2:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:00 pm[Midday Keynote] Social Engineering Defense in the Frontier AI Era Director of Product Marketing, DoppelRegistration Level:
- Open Sessions
2:00 pm - 2:45 pmAI is making social engineering attacks faster, more adaptive, and increasingly coordinated across channels. Join Doppel to explore how shared threat intelligence and AI agents connect email security, digital risk protection, and human risk management into a unified defense. Attendees will learn how this approach helps security teams identify connected threats, coordinate detection and response, and disrupt attacks across the social engineering attack chain—reducing risk while keeping pace with evolving attacker tactics.
2:45 pmNetworking BreakRegistration Level:- Open Sessions
2:45 pm - 3:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
3:00 pmAgentic AI, Controlled AutonomyTrust, Compliance, and Override Architecture for Autonomous Enterprise Agents Lead Platform Engineer, Stitch FixRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmAs enterprises push agentic AI into systems that act independently, pricing, discounting, engaging customers, and increasingly making operational decisions across the network itself, the core question shifts from “does the agent work” to “can the enterprise still trust and control it.” This session presents an architectural framework for controlled autonomy: giving agents real decision-making power while keeping enterprise governance, compliance, and security intact.
At the center is a trust layer that scores every AI-generated decision on confidence, policy alignment, and risk, enabling dynamic calibration of human involvement. Low-risk decisions get automated; high-impact ones get escalated, so autonomy scales operationally without giving up governance. Sitting alongside it is compliance-aware orchestration, validating every agent action against dynamic policy graphs in real time, so agents stay within regulatory, contractual, and internal constraints even as multiple agents interact and coordinate.
A major focus is on human override: intelligent escalation triggers and contextual decision summaries that reduce cognitive load and speed up turnaround for security and operations teams managing high-velocity, autonomous environments. We’ll also cover observability, explainability, and auditability, building a transparent decision fabric so every autonomous action stays traceable, a requirement for any security-conscious enterprise deploying agentic systems at scale.
The session closes with enterprise integration patterns, bounded autonomy gateways, and parallel decision simulation, that let organizations deploy agentic AI broadly while keeping governance and security consistent as autonomy expands across the network.
3:00 pmBuy Back Your Time: AI Triage, Real Incidents, a SecOps Case Study Sr. Manager, Cyber Security & Infrastructure, RoverRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmSecurity operations teams don’t have a headcount problem, they have a signal-to-noise problem. Over the past year, Rover’s ticket volume grew 640%—and our mean time to resolution still went down, at one point dropping four hours in a single month. This talk explains how, and then shows what that time savings actually bought us during a real attack.
First, the mechanics: we built an automated triage pipeline that connects our EDR, SIEM, and phishing tools to an LLM (Gemini). Every alert triggers a purpose-built Lambda that gathers the right context—process trees, sender domain age, login history, the underlying SIEM query—and hands it to the model with a tightly scoped prompt (including explicit instructions to treat email content as untrusted data, not commands). Within seconds, a structured verdict, reasoning, and recommended action lands as a comment on the ticket. Work that took an analyst 20-30 minutes now takes seconds, and every AI verdict is clearly labeled and still requires human sign-off before action.
Then, the case study: this summer Rover faced repeated waves of automated toll fraud—thousands of fake accounts created via disposable email domains to abuse SMS verification across international phone numbers. I’ll walk through how a cross-functional team (fraud ops, engineering, and cybersecurity) used the analyst time freed up by AI triage to focus on the harder problem: real-time network and application-layer countermeasures—domain blocking, feature-flag kill switches, and edge/WAF rules—to contain each wave within hours instead of days. You will leave this presentation with concrete actions you can take back to your organization and ways to implement without a giant budget ask.
3:00 pmGeneric Agents Won’t Save Your SOC: The Case for Custom-Built Security Agents Co-Founder & VP of Strategy, Strike48Registration Level:
- Open Sessions
3:00 pm - 3:45 pmPre-built AI agents promise to drop into any SOC and start working. Every SOC runs on its own unique log sources, detection logic, escalation paths, and risk tolerance. A generic agent encodes someone else’s assumptions about all of it. When those assumptions don’t match your environment, the agent fails.
Black-box agents add a second problem. If you can’t inspect an agent’s logic, you can’t tune it or defend its decisions to an auditor. Governance frameworks for AI assume visibility into how decisions get made.
This session makes the case for building custom security agents based on your own environment. We’ll cover what a custom agent requires, and how lean teams can build agents on top of their existing stack. We’ll also explain why agents need deterministic workflows, with model reasoning limited to defined points. Attendees will leave with a framework for building agents to fit in their SOC.
3:00 pmAI Cyber Debrief: Geopolitics, Algorithmic Warfare, and the Frontier of AI Resilience CNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
 Founding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)Registration Level:
- Open Sessions
3:00 pm - 3:45 pmArtificial Intelligence is no longer just a driver of productivity; it is the primary battlefield of modern global conflict. This session connects the dots between geopolitical volatility and the immediate risks to model integrity, data sovereignty, and cognitive security. We will examine how shifting alliances involving major powers like Russia, China, and the EU are reshaping the cyber threat landscape—specifically targeting sovereign AI clusters, decentralized compute networks, and the global semiconductor supply chain.
The discussion will pivot to the “internal” evolution of the sector, analyzing the rapid integration of Agentic AI in critical infrastructure and the resulting “black box” regulatory and privacy minefield. From state-aligned actors seeking to poison training datasets to sophisticated syndicates deploying automated exploit-generation engines, we will profile the adversaries threatening the global digital order.
Join us for a 2026 outlook that moves beyond mere ethical frameworks, offering a battle-tested strategy for maintaining operational resilience and model alignment in the face of unprecedented global instability.
3:45 pmNetworking BreakRegistration Level:- Open Sessions
3:45 pm - 4:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
4:00 pm[Closing Keynote] From Insight to Action: Navigating the Next Era of AI and Advanced ThreatsSr. Manager, Intelligence, ZscalerRegistration Level:- Open Sessions
4:00 pm - 4:45 pmThis closing keynote builds on the day’s discussion and grounds next steps in real-world data. Alex Berninger will break down the defining adversary trends Zscaler MDR observed across customers over the past year, including how threat actors are operationalizing AI to supercharge their tradecraft. This session is designed to identify top threats for you and convey exactly how these shifting dynamics should impact your strategy. The goal is to help you translate trends into a pragmatic, clear, actionable playbook to protect your organization and gain a structural advantage against AI-driven and other advanced threats.

 Doppel
 is the social engineering defense platform using AI to fight AI. Built to outpace and overpower your would-be attackers, our sophisticated AI-forensics see attacks coming and crush them at their source. We safeguard every channel and move faster than attack speed. With intelligence that constantly compounds, we’re perpetually at the forefront of social engineering defenses.
We work relentlessly to defend your brand, people, and future from whatever comes next in social engineering.
 Google Cloud Security
 provides organizations with leading infrastructure, platform capabilities and industry solutions to help them solve their most critical business problems. Google Cloud Security helps customers protect their global operations with solutions such as zero trust security, application and data protection, fraud prevention, and threat detection and response.
 KnowBe4
 empowers your workforce to make smarter security decisions every day. Trusted by over 70,000 organizations worldwide, KnowBe4 helps you strengthen your security culture and manage human risk. KnowBe4 offers a comprehensive AI-driven “best-of-suite” platform for human risk management (HRM), creating an adaptive defense layer that fortifies user behavior against the latest cybersecurity threats.
The HRM+ platform includes modules for awareness and compliance training, cloud email security, real-time security coaching, crowdsourced anti-phishing, AI Defense Agents and more. As the only global security platform of its kind, KnowBe4 transforms your largest attack surface—your workforce—into your biggest asset, actively protecting your organization against cybersecurity threats.
 Strike48
’s core mission is to help you automate the extraction of business value from server logs. The Strike48 Prospector Studio is an AI Agent Creation and Management Suite that allows you to quickly start inspecting logs with AI agents. Use our Agent creation personas to help create Agents for your purposes or you can use our professionally pre-made Agents instead!
 Zscaler
 is universally recognized as the leader in zero trust. Leveraging the largest security cloud on the planet, Zscaler anticipates, secures, and simplifies the experience of doing business for the world’s most established companies.
- Christopher Porter, PhDHead of International Security Cooperation, Google Cloud
- Keyao AnMember of Technical Staff, OpenAI
Keyao An is a Member of Technical Staff at OpenAI, where she builds enterprise identity and access capabilities for complex, large-scale products. Her work focuses on authentication, authorization, multi-IdP SSO, policy-based access control, and the safe deployment of security-critical changes. Previously at Meta, she developed AI-powered business products and safety systems. She specializes in turning complex security and enterprise requirements into resilient product capabilities that balance strong controls, operational reliability, and usable customer experiences.
- Amy YeeCDO & CDTO | Board Member & Advisor | Podcaster
Amy Yee is the Host of the Wired for Change podcast and an executive leader with more than two decades of experience at the intersection of digital transformation, cybersecurity, governance, and technology strategy. Throughout her career, she has held senior executive roles across healthcare, government, and other regulated industries, leading large-scale transformation initiatives and overseeing technology, cybersecurity, privacy, enterprise architecture, and digital strategy.
Today, Amy works with organizations across critical sectors to strengthen cyber resilience while helping leaders navigate the intersection of technology, trust, and organizational change. A frequent international keynote speaker, she is known for blending real-world experience, systems thinking, and compelling storytelling to help audiences think differently about resilience, leadership, and the future of cybersecurity.
- Nishanth SirikondaCloud Solutions Architect, FirstDay Foundation
Nishanth Sirikonda is a Cloud and Enterprise Architect and technology leader specializing in cybersecurity, cloud security, enterprise architecture, and secure digital transformation. He leads the architecture and governance of critical enterprise platforms supporting multiple nonprofit organizations, with responsibility spanning identity and access management, security architecture, enterprise applications, integrations, and cloud environments. His work focuses on applying Zero Trust principles, strengthening access controls, managing technology risk, and securely adopting emerging technologies, including AI and intelligent automation.
- James DyerHead of Threat Intelligence Lead, KnowBe4
James Dyer is the Head of Threat Intelligence Lead at KnowBe4, where he spearheads a research team focused on a wide range of cybersecurity domains, including social engineering, open-source intelligence (OSINT), organizational human-risk assessment, and the emerging ways cybercriminals are leveraging artificial intelligence.
- Sai Prasad VeluruSoftware Engineer, JPMorgan Chase
Sai Prasad Veluru is an AI researcher and software engineer with expertise in artificial intelligence, distributed systems, cloud computing, and enterprise software engineering. His work focuses on building scalable, secure, and intelligent systems that solve real-world business challenges. He has authored multiple peer-reviewed research publications with more than 360 academic citations, reflecting his contributions to AI and cloud-native technologies. He holds a master’s degree in Computer Information Systems from the University of Cincinnati and is passionate about advancing secure, trustworthy AI through both research and practical engineering.
- Cameron H. MalinCyber Behavioral Profiler, FBI (Ret.) and Modus Cyberandi
Cameron Malin, JD, CISSP, is the founder of Modus Cyberandi, a bespoke Cyber Behavioral Profiling consultancy specializing in the assessment of cyber threat actor decision making, adversary tradecraft, cyber deception, and cognitive vulnerabilities. As a retired Behavioral Profiler with the Federal Bureau of Investigation (FBI), he has more than 22 years of experience investigating, analyzing, and profiling cyber adversaries across the spectrum of criminal to national security attacks.
During his tenure in the FBI, he was the founder of both the FBI Behavioral Analysis Unit's (BAU) Cyber Behavioral Analysis Center (CBAC), the FBI BAU's methodology and application of science-based behavioral profiling and assessment to national security and criminal cyber offenders—and the BAU’s Deception and Influence Group (DIG), a uniquely trained and experienced cadre of Behavioral Profilers specialized in analyses and countermeasures to adversary cyber deception campaigns and influence operations.
He is a co-author of the authoritative cyber deception book, "Deception in the Digital Age: Exploiting and Defending Human Targets Through Computer-Mediated Communications" (published by Academic Press, an imprint of Elsevier, Inc.), and co-author of the Malware Forensics book series: "Malware Forensics: Investigating and Analyzing Malicious Code," "Malware Forensics Field Guide for Windows Systems," and "Malware
Forensics Field Guide for Linux Systems" (all published by Syngress, an imprint of Elsevier, Inc.). - Josh BartolomieVP, Global Threat Intelligence, Doppel
With over 26 years of experience in information technology and cybersecurity, Josh has developed extensive expertise in designing and implementing security operations centers, incident response teams, and robust security architectures. He has also led the establishment of multiple teams and programs focused on compliance, risk management, and security strategy for many large global organizations, including ITT Inc., Exelis, L3Harris, and Cognizant.
Throughout his career, Josh has remained dedicated to data-driven research and innovation, with a focus on developing solutions that address real-world security gaps and deliver immediate, measurable value for cybersecurity defenders and organizations worldwide. His leadership is marked by a strong commitment to enhancing security resilience, promoting risk awareness and reduction, and safeguarding businesses against both current and emerging threats.
- Alex BerningerSr. Manager, Intelligence, Zscaler
Alex has worked in the threat intelligence field for 18 years and specializes in taking complicated technical jargon and translating it into a form that is engaging, approachable, and actionable to the end reader. Within cybersecurity intelligence, she has worked a variety of roles, including threat hunter, analyst, product owner, customer success lead, and manager.
- Alvin LinDirector of Product Marketing, Doppel
Product Marketing Leader built for uncharted territory: I turn chaos into structured, repeatable go-to-market success. Currently leading Product Marketing at Doppel with a mission to protect our AI-driven world from evolving social engineering attacks every day. My team’s role is to be the force multiplier that accelerates enterprise outcomes by leading the Social Engineering Defense category through messaging, positioning, competitive intelligence, product and feature launches, pricing and packaging, and analyst relations.
Deep expertise scaling companies toward $1B ARR and beyond, specializing in architecting first-of-its-kind pre-sale motions and post-sale programs that accelerate revenue and net retention. I deeply believe the go-to-market engine must scale results by design, not by chance, which has driven my success architecting growth strategies for pipeline generation and revenue across the full customer lifecycle.
- Surajit PaulLead Platform Engineer, Stitch Fix
- Nick BakerSr. Manager, Cyber Security & Infrastructure, Rover
- Tim LeehealeyCo-Founder & VP of Strategy, Strike48
Tim Leehealey is the Co-founder and VP of Strategy at Strike48, an agentic operations platform for security and IT teams. With 25+ years in security operations and forensics, Tim has spent his career at the intersection of detection engineering and data architecture. His career spans both finance and technology, starting with six years in banking at JPMorgan Investment Management. Since transitioning to the tech industry, he’s held pivotal executive roles including CEO and Chairman of the Board at AccessData. His dual expertise in business leadership and technology underscores his commitment to fostering innovation in the cybersecurity and IT sectors.
- Col. Cedric LeightonCNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
Cedric Leighton is a CNN Military Analyst and a retired United States Air Force Colonel. On CNN, he has provided incisive commentaries on the Israel-Hamas War, the War in Ukraine, the U.S. withdrawal from Afghanistan, and numerous other conflicts around the world. His analysis has been seen by millions of viewers around the world and provided much needed context to some of the most pressing national security issues of our time. As a U.S. Air Force officer, Colonel Leighton served at U.S. Special Operations Command, the Joint Staff, and the National Security Agency, where he helped train the nation's cyber warriors. A Middle East combat veteran, he is the recipient of numerous military awards, including the Defense Superior Service Medal and the Bronze Star. After serving 26 years as a U.S. Air Force Intelligence Officer, Col. Leighton founded a strategic risk consultancy and became the co-founder of CYFORIX, where he advises multinational businesses on developing better cyber strategies designed to reduce risk and unpredictability.
- VJ ViswanathanFounding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)
VJ Viswanathan is a global technology and security executive with more than 25 years of experience spanning AI, cloud and enterprise platforms, cybersecurity, privacy, and technology risk. He has held senior executive roles at large enterprises, including Keurig Dr Pepper, Comcast, HD Supply, and GE, where he led technology, cybersecurity, privacy, and risk programs across highly complex and distributed environments.
Today, VJ works with boards and executive teams on the security challenges created by AI, automation, and digital sprawl—helping leaders understand where traditional security models fall short and how to adapt. He currently serves as Founding Partner of CYFORIX and CEO of TORQE, focused on strategic defense and enterprise transformation.
- Alex BerningerSr. Manager, Intelligence, Zscaler
Alex has worked in the threat intelligence field for 18 years and specializes in taking complicated technical jargon and translating it into a form that is engaging, approachable, and actionable to the end reader. Within cybersecurity intelligence, she has worked a variety of roles, including threat hunter, analyst, product owner, customer success lead, and manager.